Challenges and innovations shaping the evolution of digital security today.
Services / Consulting
Consulting
Services
Strategic and technical advisory that turns regulatory pressure into competitive advantage — and risk into resilience.
Advisory
GRC
Compliance
ISO · DORA · NIS2
Risk
ISO 31000
Governance
Audit · DPO
Strategy
CISO · PMO
About Consulting Services
Specialized Advisory
A specialized advisory service that delivers tailor-made solutions and strategic and technical support — focused on guaranteeing compliance, mitigating risk and strengthening cybersecurity posture.
We provide rapid, continuous technical support through a close, experienced team that backs your audits, certifications and integrations from end to end.
What sets us apart
Areas of Expertise
What we Offer
Architecture
The Advisory Framework
Advisory
GRC
Consulting
Compliance
ISO · DORA · NIS2
Risk Management
ISO 31000
Strategy
CISO · PMO
Compliance
ISO · DORA · NIS2 — Verification of process alignment with internal policies and external regulations, identifying gaps and delivering corrective recommendations.
Risk Management
ISO 31000 — Risk assessment by process and workflow, with reinforced continuous monitoring and automation proposals for alerting and incident response.
Strategy
CISO · PMO — Integration of compliance best practices into business processes, minimizing operational, regulatory and reputational risks.
Detail
Services in detail
Process Compliance
Process Compliance
We verify the alignment of your processes with internal policies and external regulations, identifying gaps and delivering corrective recommendations.
01
Alignment Verification with DORA, EBA, BdP
Verification of process alignment with internal policies and external regulations.
02
Gap Identification & Corrective Recommendations
Identifying gaps and delivering actionable corrective recommendations.
03
Process Mapping & Control Implementation
Mapping processes and implementing controls to guarantee process and control auditability.
04
Internal Audit Execution
Support for management systems ISO 9001, ISO 14001 and ISO 45001.
Frameworks
→ cyberwatch --assess --framework dora
✓ DORA articles mapped: 64/64
✓ Control gaps identified: {{ DORA_GAPS }}
✓ Maturity score: {{ DORA_SCORE }}/5
→ scan --framework nis2 --scope your-business.com
⚠ Reviewing essential entity scope...
⚠ Mapping critical functions...
⚠ Assessing incident reporting readiness...
→ contact --team cyberwatch
Connecting to SIBS Cyberwatch...
Start your compliance journey
Discover how to align your organization with the latest regulatory and cybersecurity requirements.
News
Latest News
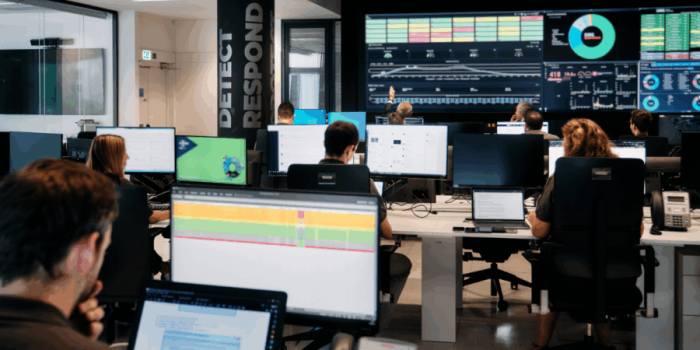
Integrating technology, people and processes is the key to secure innovation
Leadership in cybersecurity and innovation.