Challenges and innovations shaping the evolution of digital security today.
Services / Cyber Defence
Cyber Defence
Detecting and neutralizing threats at the earliest stage is decisive in preventing a cyber attack.
Threats Blocked
+{{ THREATS_BLOCKED_YEAR }} last year
SOC Status
LIVE 24/7
Response Time
< {{ RESPONSE_SLA_HOURS }}h
ABOUT Cyber Defence
Managed Detection & Response
Managed Detection & Response (MDR) combines endpoint, network and cloud monitoring with threat intelligence and behavioral analytics to continuously validate your organization’s security posture.
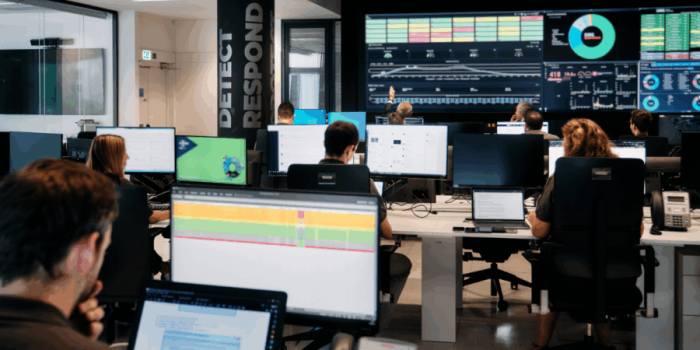
We monitor signals from multiple systems and sources, detect incidents and respond immediately by isolating affected systems wherever they are. Powered by 24×7 Security Operations Centers (SOC), our MDR is backed by a dedicated team of cybersecurity analysts and engineers with proven experience protecting the most critical national infrastructures.
Incidents assessed per year
Number of protected endpoint assets
Cases threat hunting per year
Capabilities
Monitoring, Detection & Response
Monitoring
Detection
Response
Architecture
The Pillars of Cyber Defence
SOCSecurity Operations
EDREndpoint Detection
CTIThreat Intelligence
MDR
Defence
Endpoint Detection and Response (EDR)
Monitors endpoints — the primary target for attacks and intrusion attempts.
Security Operations Centers (SOC)
People, processes and technology built to deliver 24×7 monitoring, detection, triage, investigation and incident response.
Cyber Threat Intelligence (CTI)
Detects exposed and at-risk assets, identifies data loss, raises alerts and contextualizes indicators of compromise.
Detail
The pillars in detail
Security Operations Center
Security Operations Center (SOC)
A team dedicated to supporting our clients in building a mature cybersecurity and information security strategy.
01
24/7 Monitoring & Detection
Continuous scans across networks, devices and applications, using SIEM and complementary tools to identify signs of security breaches.
02
Incident Response
When a threat is detected, the SOC team acts quickly to contain and neutralize it, minimizing business impact.
03
Threat Hunting
Proactively searches for potential vulnerabilities or undiscovered intruders inside the network.
04
Compliance & Log Management
Maintains comprehensive activity logs to ensure regulatory compliance and analyze past incidents.
This service includes
End-to-End Coverage
The full Cyber Defence lifecycle
From signal collection to threat neutralization — we cover every stage of the attack lifecycle with specialized capabilities and immediate response.
→ cyberwatch --status
✓ SOC operational · 24/7 active
✓ Threat feeds: 142 active sources
✓ SIEM correlation: LIVE
→ scan --target your-business.com
⚠ Running surface analysis...
⚠ Checking credential leaks...
⚠ Analysing exposure vectors...
→ contact --team cyberwatch
Connecting to SIBS Cyberwatch...
Protect your business today
Discover how to protect critical systems, networks and data 24/7 and increase your company’s digital resilience.
NEWS
Latest News
Integrating technology, people and processes is the key to secure innovation
Leadership in cybersecurity and innovation.